

Email security built for mid-market teams
Sublime is agentic email security that tailors itself to your environment, so a small team can cover what used to take a much larger one.
What challenges do mid-size security teams face?
Most email security tools were built for organizations with a large dedicated security team, or for those with almost none. Mid-size teams fall through the gap.
Threat volume that outpaces the team
Mid-size security teams can't afford to manually triage every reported email. When the abuse mailbox fills faster than the team can respond, real threats sit unreviewed while analysts burn time on obvious junk.

Defenses that can't keep up with attackers
Legacy secure email gateways and first-generation AI tools apply the same detection logic across every customer. Attackers learn to evade it. Mid-size teams absorb the false positives and misses without the resources to retrain. The attacks doing the most damage today are targeted social engineering, vendor fraud, and thread hijacking: precisely the ones generic detection is slowest to catch.
No visibility into why decisions get made
When a threat gets through or a legitimate email gets blocked, teams need to understand why. Black-box platforms offer post-hoc explanations, not the actual logic that drove the verdict. That gap compounds over time.
How Sublime supports mid-size security teams
Sublime gives mid-size teams enterprise-grade protection without the headcount. Investigation and response run autonomously so your analysts focus on what actually needs them.
Automate investigation and response across the abuse mailbox
ASA (Autonomous Security Analyst) triages user-reported email in seconds. Instead of analysts working through a queue, ASA investigates, applies a verdict, and remediates confirmed threats automatically, escalating only the cases that actually need human attention.
Get visibility into every decision
Every Sublime verdict traces to specific signals and transparent detection logic. Mid-size teams can see exactly what triggered a decision, tune exceptions without opening a vendor ticket, and audit the full detection history at any time.
Close coverage gaps in hours, not vendor cycles
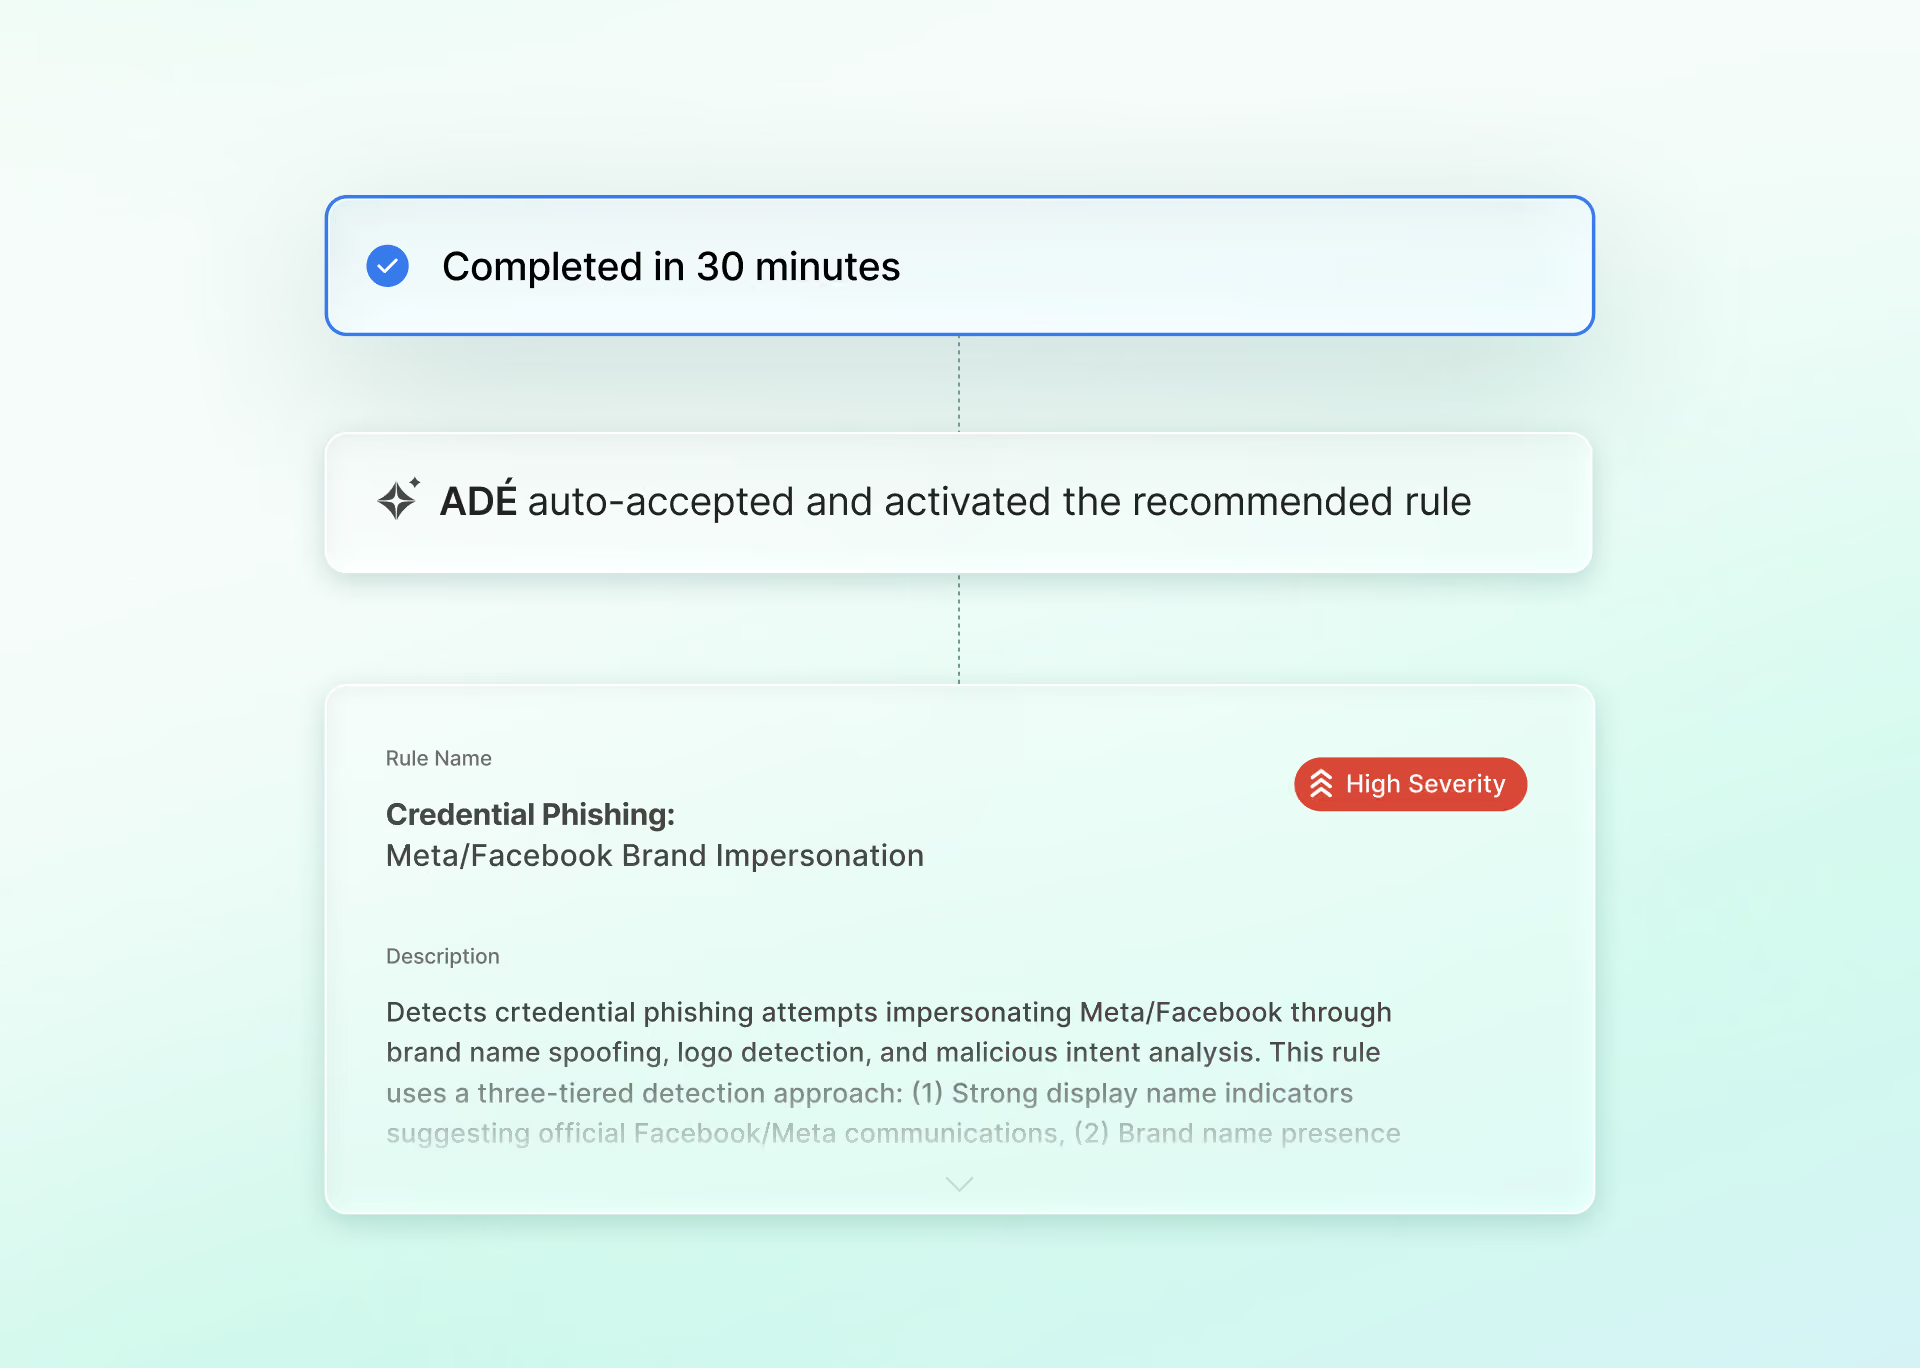
ADÉ (Autonomous Detection Engineer) generates org-specific detections based on threats seen in your environment. When a new attack pattern emerges, ADÉ turns around new coverage in hours, not weeks. Mid-size organizations don't need detection engineers on staff to get that speed.
One platform across every direction email flows
Sublime covers inbound, outbound, and internal email in a single deployment. No add-on modules for DLP. No separate tool for threat hunting. One platform, full coverage, without the overhead of managing multiple vendor relationships.
Why mid-size teams choose Sublime
Legacy gateways and first-gen AI weren't built for targeted attacks at your size. That's the gap Sublime fills.
Coverage built for your environment
Centralized models generalize across all customers, so every customer inherits the same blind spots. Sublime's Distributed Detection Model runs org-specific coverage that isn't averaged down by the rest of the market.


Decisions you can see and act on
Most platforms return a verdict with no visible logic. When something goes wrong, you file a ticket. Sublime shows the exact detection logic behind every decision, so your team can resolve issues without waiting on a vendor.

Coverage gaps that close in hours
When a new attack pattern emerges, centralized vendors update on their own schedule. ADÉ generates and deploys new detections based on threats in your environment, closing gaps in hours.
Email security capabilities for mid-market organizations
Inbound threat detection
Inbound email analysis covers BEC, vendor impersonation, credential phishing, thread hijacking, and the emerging attack variants that one-size-fits-all platforms are slowest to catch. These are the attacks designed to look legitimate to a generic model: targeted at your specific vendors, your org chart, your financial workflows. Sublime's org-specific coverage catches them because it's built around your environment, not a shared baseline.
Agentic email security
ASA investigates every user-reported email and remediates confirmed threats automatically, without an analyst queue. ADÉ generates and deploys new detections when novel attack patterns emerge, closing coverage gaps without waiting on a vendor update cycle. Both agents run continuously and escalate only when human judgment is needed.
Sublime's Email DLP monitors outbound and internal email for sensitive data exposure, credential leaks, and policy violations that traditional inbound-only email security misses entirely. Outbound and internal threats such as an employee exfiltrating data before leaving, a misconfigured auto-forward rule, or a credential shared over email are not caught by platforms focused only on what comes in. One platform covers every direction email moves.
Threat hunting and investigation
Search across historical email, hunt by TTPs, and backtest detection changes against past traffic to investigate events and validate updates before rollout. When a new attack pattern is identified, Sublime can surface whether that pattern already reached your inbox, giving mid-size teams threat hunting capability without dedicating analyst time to run it manually. Every investigation runs against the same email archive used for day-to-day detection.
Fits your stack
API deployment to Microsoft 365 or Google Workspace with no MX record changes required, plus SIEM, SOAR, and Slack integrations that fit into the workflows your team already uses. No appliance to configure, no mail flow disruption during rollout, and no dedicated migration window. Sublime connects to your environment and your existing security tools, not the other way around.
Proof from real teams
95%
of user-reported emails auto-remediated through ASA

80%
faster user report investigation

~100hours
reclaimed annually by analysts

See Sublime in your environment

Related resources

FAQs about email security for mid-market organizations
What should mid-market organizations look for in an email security solution?
Coverage quality and gap closure speed matter most: specifically, whether the platform catches targeted, context-rich attacks that weren't in the training data, and whether it closes new coverage gaps without waiting on a vendor update cycle. Beyond protection, look for visibility into why decisions get made, operational efficiency that reduces investigation workload rather than adding to it, and low deployment overhead. Tools that require heavy configuration or ongoing tuning are designed for teams with time to babysit them. Most mid-size teams don't have that.
What is the best email security software for mid-market organizations?
The right platform catches targeted, org-specific attacks that generic models miss, closes coverage gaps in hours rather than vendor update cycles, and gives your team visibility into every decision without requiring a ticket. Sublime is built around all three. Two AI agents handle the work that would otherwise require dedicated headcount: ASA (Autonomous Security Analyst) triages and remediates threats in seconds, and ADÉ (Autonomous Detection Engineer) generates new detection coverage in hours when the threat landscape shifts.
Does Sublime integrate with Microsoft 365 and Google Workspace for mid-size companies?
Yes. Sublime integrates natively with both Microsoft 365 and Google Workspace via API, with no MX record changes or infrastructure modifications required. Mid-size organizations can connect Sublime to their existing email platform and begin receiving protection within hours. Sublime adds a tailored detection and response layer on top of native platform security, catching the targeted attacks that Microsoft Defender and Google's built-in tools routinely miss.
How does Sublime help mid-size security teams reduce email security workload?
The primary mechanism is automation. ASA investigates every user-reported email, applies a verdict, and remediates confirmed threats automatically, without an analyst needing to touch it. Teams that previously spent hours each week clearing the abuse mailbox get that time back. In parallel, ADÉ generates new coverage when novel threats emerge, so mid-size teams aren't left waiting weeks for a vendor update. Customers have seen a 96% reduction in manual investigations and approximately 100 analyst hours reclaimed annually after deploying Sublime.
Is Sublime difficult to set up and manage for a mid-size security team?
No. Sublime deploys via API with no MX record changes required. There's no appliance to configure, no complex policy tuning required to get started, and no ongoing maintenance burden that falls on the security team. Once deployed, the platform runs autonomously: ASA handles triage, ADÉ generates new coverage, and the team steps in when they want to, not because the tool requires it.
When should mid-size companies consider layering Sublime with existing email security tools?
Many mid-size organizations run Sublime alongside Microsoft 365's native email security or an existing gateway. Because Sublime deploys via API with no MX changes, it adds tailored detection coverage without disrupting existing mail flow or requiring a rip-and-replace. Teams typically add Sublime when they're seeing false negatives their current platform isn't catching, when they need abuse mailbox automation, or when they want detection visibility and control their existing vendor doesn't offer.
Can Sublime replace our existing email security tools?
For most mid-market organizations, yes. Sublime covers inbound threat detection, automated investigation and response, Email DLP for outbound and internal email, and threat hunting in a single platform. US Signal consolidated from three separate tools to Microsoft 365 plus Sublime, reducing email security spend by more than 70%. Whether Sublime replaces your existing stack or layers on top of it depends on your current setup. Because Sublime deploys via API with no MX changes, the evaluation itself is low-friction: run it alongside your current tools, see what it catches that your stack misses, and make the decision based on what you find.
How does Sublime handle the growing volume of AI-generated phishing attacks?
AI-generated attacks are one of the fastest-growing threats in email security: signals of AI-generated content in malicious emails grew roughly 5x across 2025. Generic detection logic struggles when attackers can generate novel, personalized content at scale. Sublime builds org-specific coverage that detects behavioral and structural signals in email rather than relying on pattern matching against known attack templates. That approach is more durable against AI-generated attacks than platforms trained on historical threat data alone.
Now is the time
See how Sublime delivers autonomous protection by default, with control on demand.