
Enterprise anti-phishing software built for modern email attacks
Sublime's agentic email security platform catches credential theft, QR codes, calendar invites, callback scams, and BEC, then adapts to the attacks your organization sees.
Phishing in a nutshell
Phishing isn't one attack pattern anymore. It's a category of techniques that share a goal, getting a person to click, reply, scan, or call, and little else in how they're built.That range is what makes phishing hard to stop with one detection method. A platform tuned for link-based credential theft can still miss a QR code, a calendar invite, or a BEC email that carries no malicious payload at all, just a convincing request. Static rules and centrally maintained models fall further behind every time attackers introduce a new variant, and introducing a new variant now takes far less effort than it used to.
Why phishing keeps getting through
Most anti-phishing tools were built to catch the attacks of a few years ago. Here's what's changed.
Attacks are built for your organization, not a generic target
Nearly 90% of malicious emails are customized to their target organization, according to Sublime's Email Threat Research Report, which is why static, centrally maintained rules fall behind.
AI is accelerating how fast lures change
Signals of AI-generated phishing content jumped roughly 5x between Q1 and Q4 of 2025, per the same Email Threat Research Report, so a rule written for last quarter's lure often misses this quarter's version.
Attackers keep finding new delivery methods
QR codes and calendar invites route around filters built to scan links and text. QR code attacks grew 282.7% in the second half of 2025, and ICS phishing grew roughly 100x over the same year, per Sublime's threat research.
Broader coverage can mean more work, not less
Detecting more only helps if it doesn't flood the SOC. Coverage needs to come paired with automated triage, not just more alerts.
Phishing techniques Sublime protects against
Credential phishing
Impersonates a login page or trusted brand to harvest usernames, passwords, and MFA codes. Attackers rotate domains constantly, stand up lookalike infrastructure within hours, and build pages that are visually identical to the real thing, so a quick glance often isn't enough to catch them. Sublime checks sender authentication (SPF, DKIM, DMARC) alongside computer vision and language analysis, weighing what a message claims to be against what the infrastructure behind it actually shows, to catch impersonation that clears authentication checks on its own.
QR code phishing
Hides a malicious link inside a QR code, often in an image or PDF attachment, to route around filters built to scan visible text and links. QR codes also move the attack off a monitored device, since a person usually scans with a personal phone, outside any corporate security stack, which is part of why this technique has grown so fast. Sublime decodes embedded QR codes during analysis and evaluates the resulting destination with the same scrutiny applied to a direct link.
ICS phishing
Delivers a malicious calendar invite instead of an email, exploiting the fact that many tools don't inspect ICS attachments closely and that invites carry an implicit trust an ordinary email doesn't. A convincing invite can auto-populate a victim's calendar before anyone has scrutinized it the way they would a suspicious message. Sublime applies the same scrutiny to invite metadata, sender legitimacy, and embedded links that it applies to email body content, closing a gap many tools leave open.
Callback phishing
Uses an email with no malicious link, just a phone number and a plausible pretext like an invoice, a subscription renewal, or a fraud alert, to move the attack to a live phone call where a person is socially engineered in real time. Because the email itself carries no payload, link and attachment scanning has nothing to flag. Sublime's language models read the urgency and pretext patterns that typically precede a callback, correlated against sender history, to catch what link-only scanning would miss.
Business email compromise
Impersonates an executive, vendor, or partner to redirect a payment, change banking details, or extract sensitive data, often with no attachment or link at all, just a convincingly worded request. BEC and fraud account for nearly one in three confirmed email threats, per Sublime's Email Threat Research Report, and thread hijacking, quietly inserting a fraudulent reply into an existing conversation, is the leading technique behind it. Sublime's relationship and behavior analysis flags spoofed domains, unusual payment requests, and hijacked threads that a generic rule set would read as ordinary correspondence.
How Sublime detects advanced phishing
Broad coverage only matters if the detection behind it holds up against attacks built to look legitimate. Here's what happens before Sublime reaches a verdict.
Every message is checked against the sender's history with your organization: domain age, prior contact, and whether the claimed relationship (vendor, executive, partner) matches what Sublime has actually observed.
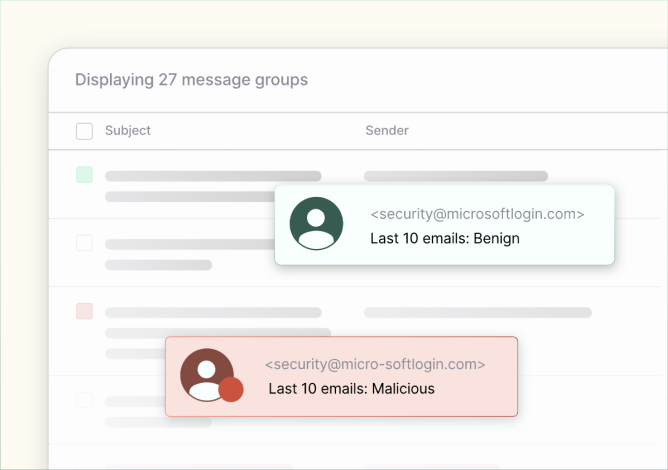
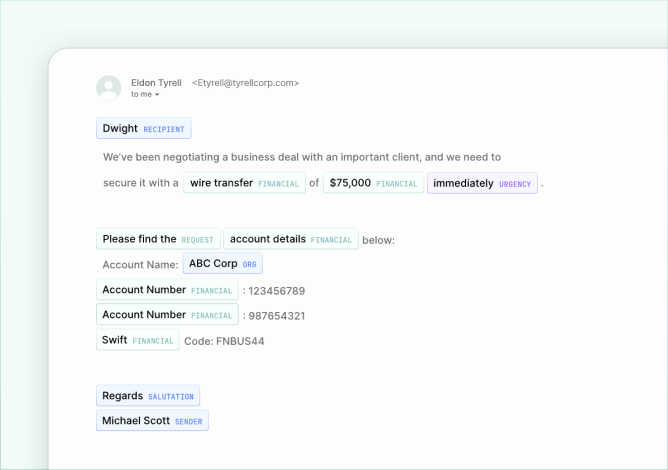
Natural language understanding reads what a message is asking the recipient to do, whether that's urgency around a wire transfer or pressure to call a number, catching BEC and callback attempts with no malicious link to scan.
Computer vision decodes QR codes, evaluates visual similarity to known brands, and follows link redirects to the actual destination rather than trusting a reputation score alone.
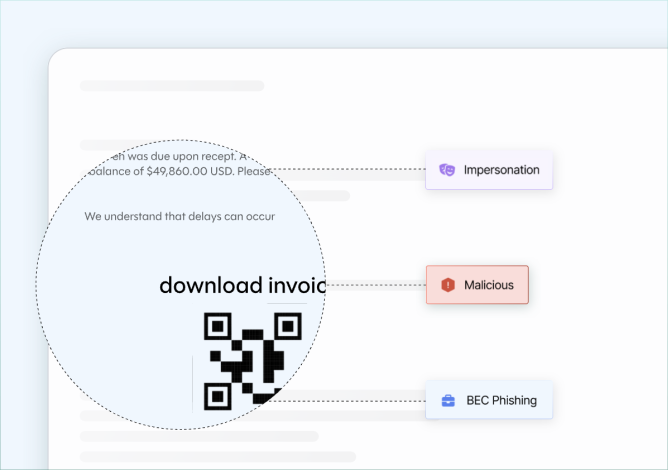
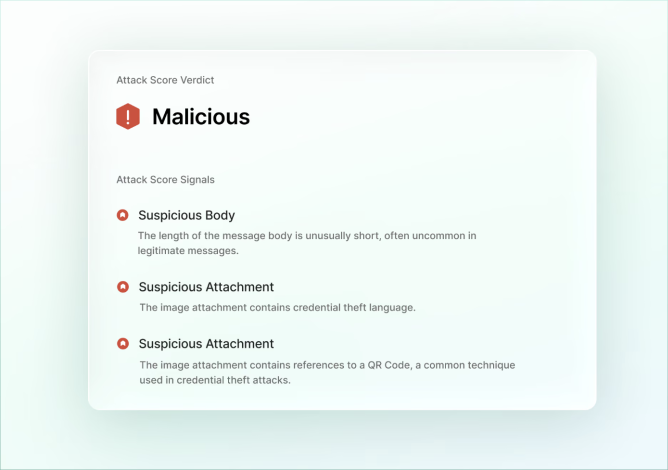
Sender behavior, language, visual analysis, and link data are weighed together before Sublime generates detection logic. Every verdict traces back to the exact signals and reasoning that produced it, so analysts can check the work.
Phishing protection that adapts to your organization
Coverage that's broad but generic still misses the attacks built specifically for your organization. Here's what adapts it.
Organization-specific detection
ADÉ (Autonomous Detection Engineer) generates new detection logic based on the attacks your organization actually sees. Coverage reflects your specific environment, not a baseline shared across every customer on the platform.
Nuanced industry expertise
Phishing tactics vary by sector: more BEC and wire-fraud attempts in financial services, more credential phishing aimed at SSO in SaaS, higher-volume low-sophistication attacks in education. Sublime tailors detection and reporting accordingly.
Transparent detection logic
Every verdict is auditable. Analysts see the exact signals and detection logic behind a decision, not a plausible explanation generated after the fact.
Autonomous detection engineering
When Sublime's agents encounter a new phishing pattern, ADÉ authors and backtests new detection logic against historical traffic before it ever reaches production, so new coverage doesn't come at the cost of new false positives.
How does Sublime's anti-phishing software compare to traditional protection?
The differences aren't about any single feature. They show up in how detection is built and who it's built for.
Prevent phishing without creating more work for the SOC
96%
reduction in manual investigations


~40hrs/week
of analyst time reclaimed from phishing response

20x
more attacks detected
Advanced phishing protection for your organization
See how Sublime's platform safeguards your business against phishing across every technique attackers use.

Latest on phishing
Frequently asked questions
What is anti-phishing software?
Anti-phishing software detects and blocks deceptive emails designed to steal credentials, deliver malware, or manipulate a recipient into an action like a wire transfer or gift card purchase. Older tools focused mainly on scanning links and attachments for known bad indicators. Modern platforms go further: they analyze sender behavior, language and intent, images, and QR codes across the full range of phishing techniques, including attacks that carry no malicious payload at all, like many business email compromise attempts. The goal is the same either way, stop the message before someone acts on it, but the detection now has to cover far more ground than link scanning alone.
How does anti-phishing software work?
It analyzes incoming messages for signals of deception: spoofed or unfamiliar sender domains, urgent or manipulative language, mismatched links, and suspicious images or QR codes. Rather than checking each signal in isolation, effective platforms weigh them together before deciding whether a message is safe, suspicious, or malicious. Sublime's agents follow that pattern and go a step further, generating organization-specific detection logic based on the attacks a given company actually sees rather than applying one static rule set to every customer on the platform. That distinction, tailored coverage versus a generic baseline, is often what separates a platform that catches a novel attack from one that lets it through.
What types of phishing can anti-phishing software detect?
Full-coverage platforms detect credential phishing (fake login pages built to steal passwords and MFA codes), QR code phishing (malicious links hidden inside scannable images), ICS or calendar-invite phishing (invites that bypass tools built to scan email content), callback phishing (a phone number instead of a link, meant to move the attack to a live call), and business email compromise (impersonation used to redirect payments or data, often with no attachment or link at all). Coverage varies significantly by vendor, so it's worth confirming a platform detects all five rather than assuming broad "phishing protection" covers each one equally well.
Can anti-phishing software detect attacks without malicious links?
Yes, when it analyzes language and intent rather than relying only on link and attachment scanning. Callback phishing and many business email compromise attempts carry no malicious payload at all, just a phone number or a convincingly worded request, so there's nothing for a traditional scanner to flag. Detecting these attacks means understanding what a message is actually asking the recipient to do, whether that's pushing urgency around a wire transfer, requesting a call back, or impersonating a vendor's normal invoicing pattern. Platforms built around signature and link scanning alone will consistently miss this category of attack.
Can anti-phishing software detect zero-day phishing?
It depends on how the platform's detection is built. Tools that rely on static, centrally maintained rules struggle with genuinely new techniques until the vendor's next scheduled update closes the gap, which can leave an organization exposed for days or weeks. Platforms built around adaptive, organization-specific detection close that window faster: Sublime's ADÉ (Autonomous Detection Engineer) generates and deploys new detection logic in hours when a novel pattern appears, backtested before it goes live, rather than waiting on a centralized model to catch up. The speed of that response, not just the breadth of existing coverage, is what determines how exposed an organization stays to a brand-new attack pattern.
What should enterprises look for in anti-phishing software?
Look for full coverage across attack types, not just link-based credential phishing: QR codes, calendar invites, callback scams, and BEC all need dedicated detection. Look for detection that adapts to your organization rather than a one-size-fits-all model shared across every customer on the platform, since nearly 90% of malicious emails are customized to their target. Look for transparent reasoning behind every verdict, so analysts can validate a decision instead of trusting a risk score with no logic behind it. And look for automated triage that scales with expanded coverage, so catching more doesn't mean an analyst reviewing more alerts every week.
How is anti-phishing software different from a spam filter?
Spam filters are built to catch unwanted bulk email, newsletters, promotions, mass-blasted junk, mostly by looking at volume, sender reputation, and known bad patterns. Phishing is built to look wanted. A well-crafted credential phishing email or BEC attempt is addressed to one person, references real context, and is designed to pass exactly the checks a spam filter uses. Anti-phishing software has to reason about intent and relationship instead: what the message is asking the recipient to do, and whether the claimed sender matches what's actually known about them. That's a different problem than filtering bulk mail, and it needs different detection entirely.
How effective is anti-phishing software at stopping attacks?
Effectiveness varies widely by how the detection is built. Platforms relying on static rules and known indicators catch familiar attacks reliably but miss novel ones until a vendor updates the model. Adaptive, organization-specific detection closes that gap: Sublime customers have reported detecting 20x more attacks, with a 96% reduction in manual investigations, because expanded coverage is paired with automated triage from the start. The more useful question isn't a single effectiveness percentage, since that figure depends heavily on which attacks are being measured. It's whether a platform's coverage and workload keep pace with each other as attacks evolve.
Now is the time
See how Sublime delivers autonomous protection by default, with control on demand.