Save time and reduce MTTR with an automated, customizable, and extensible abuse mailbox powered by intelligent email security.

Ensure that user-reported emails are handled quickly and accurately.
Automatically close the loop
After a recipient reports a suspicious message, they’re automatically notified when the message has been triaged and classified.
Autonomous triage
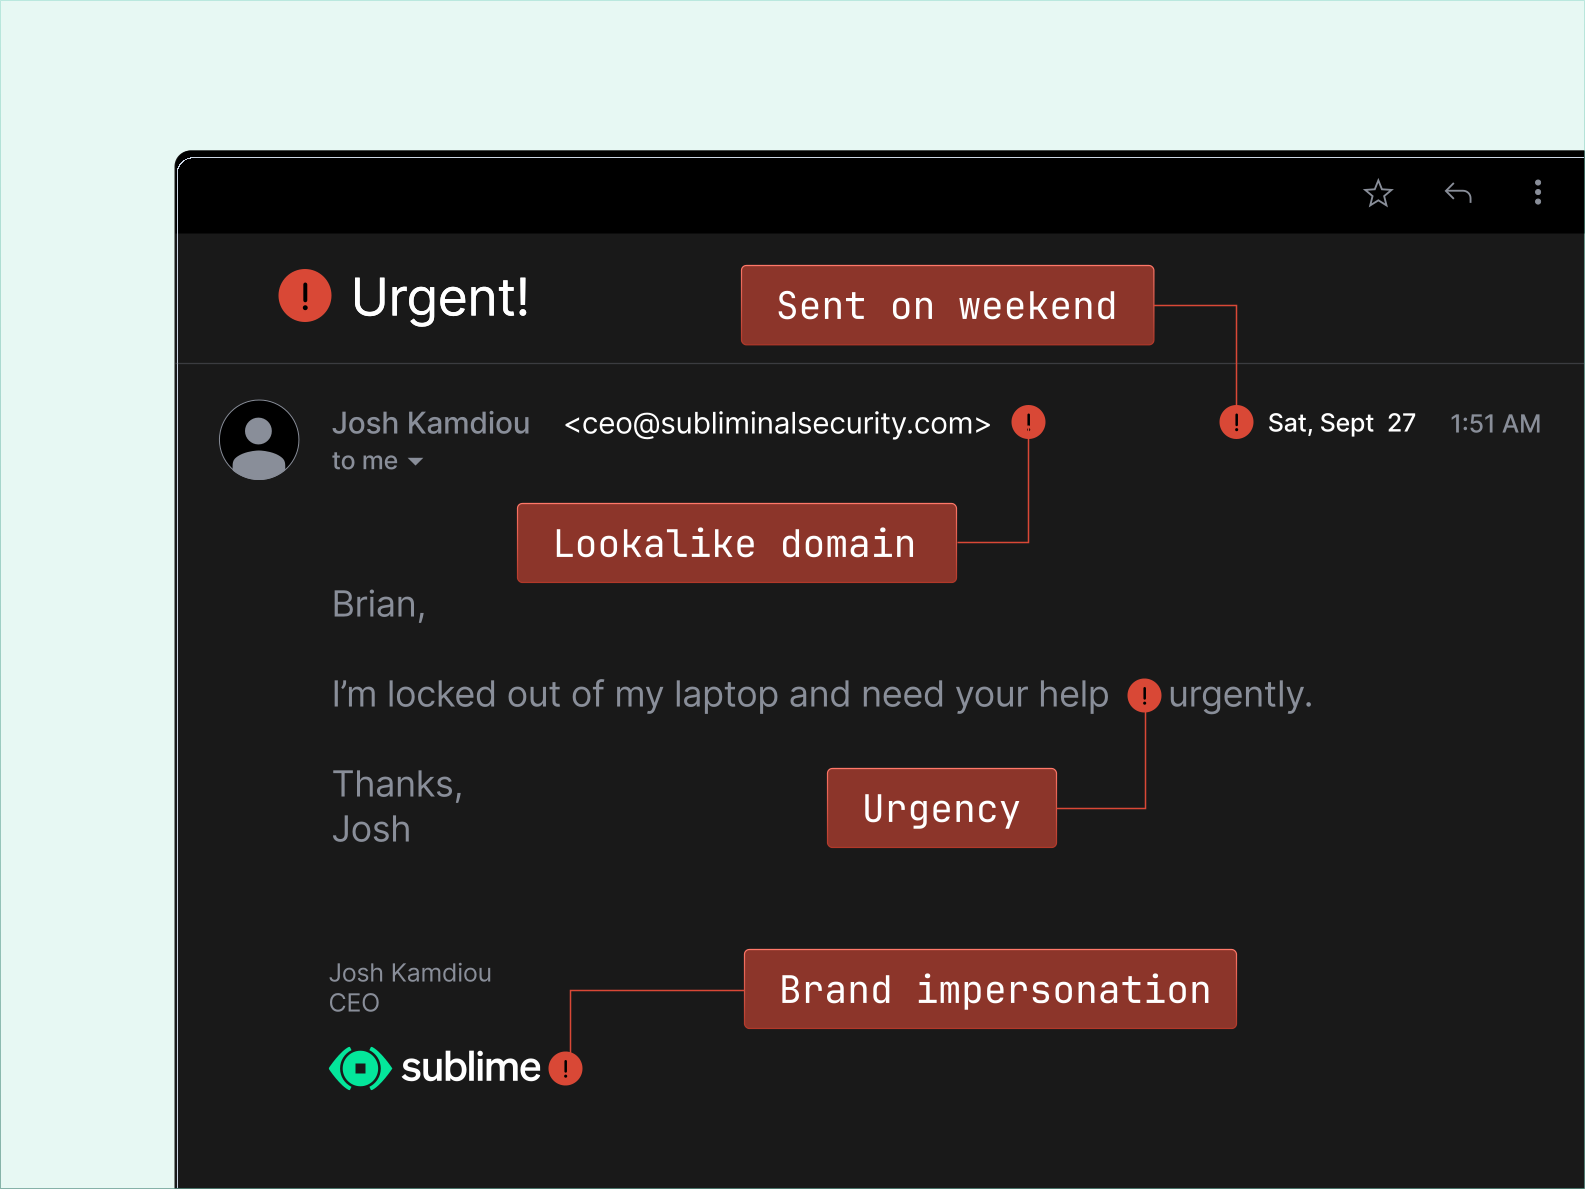
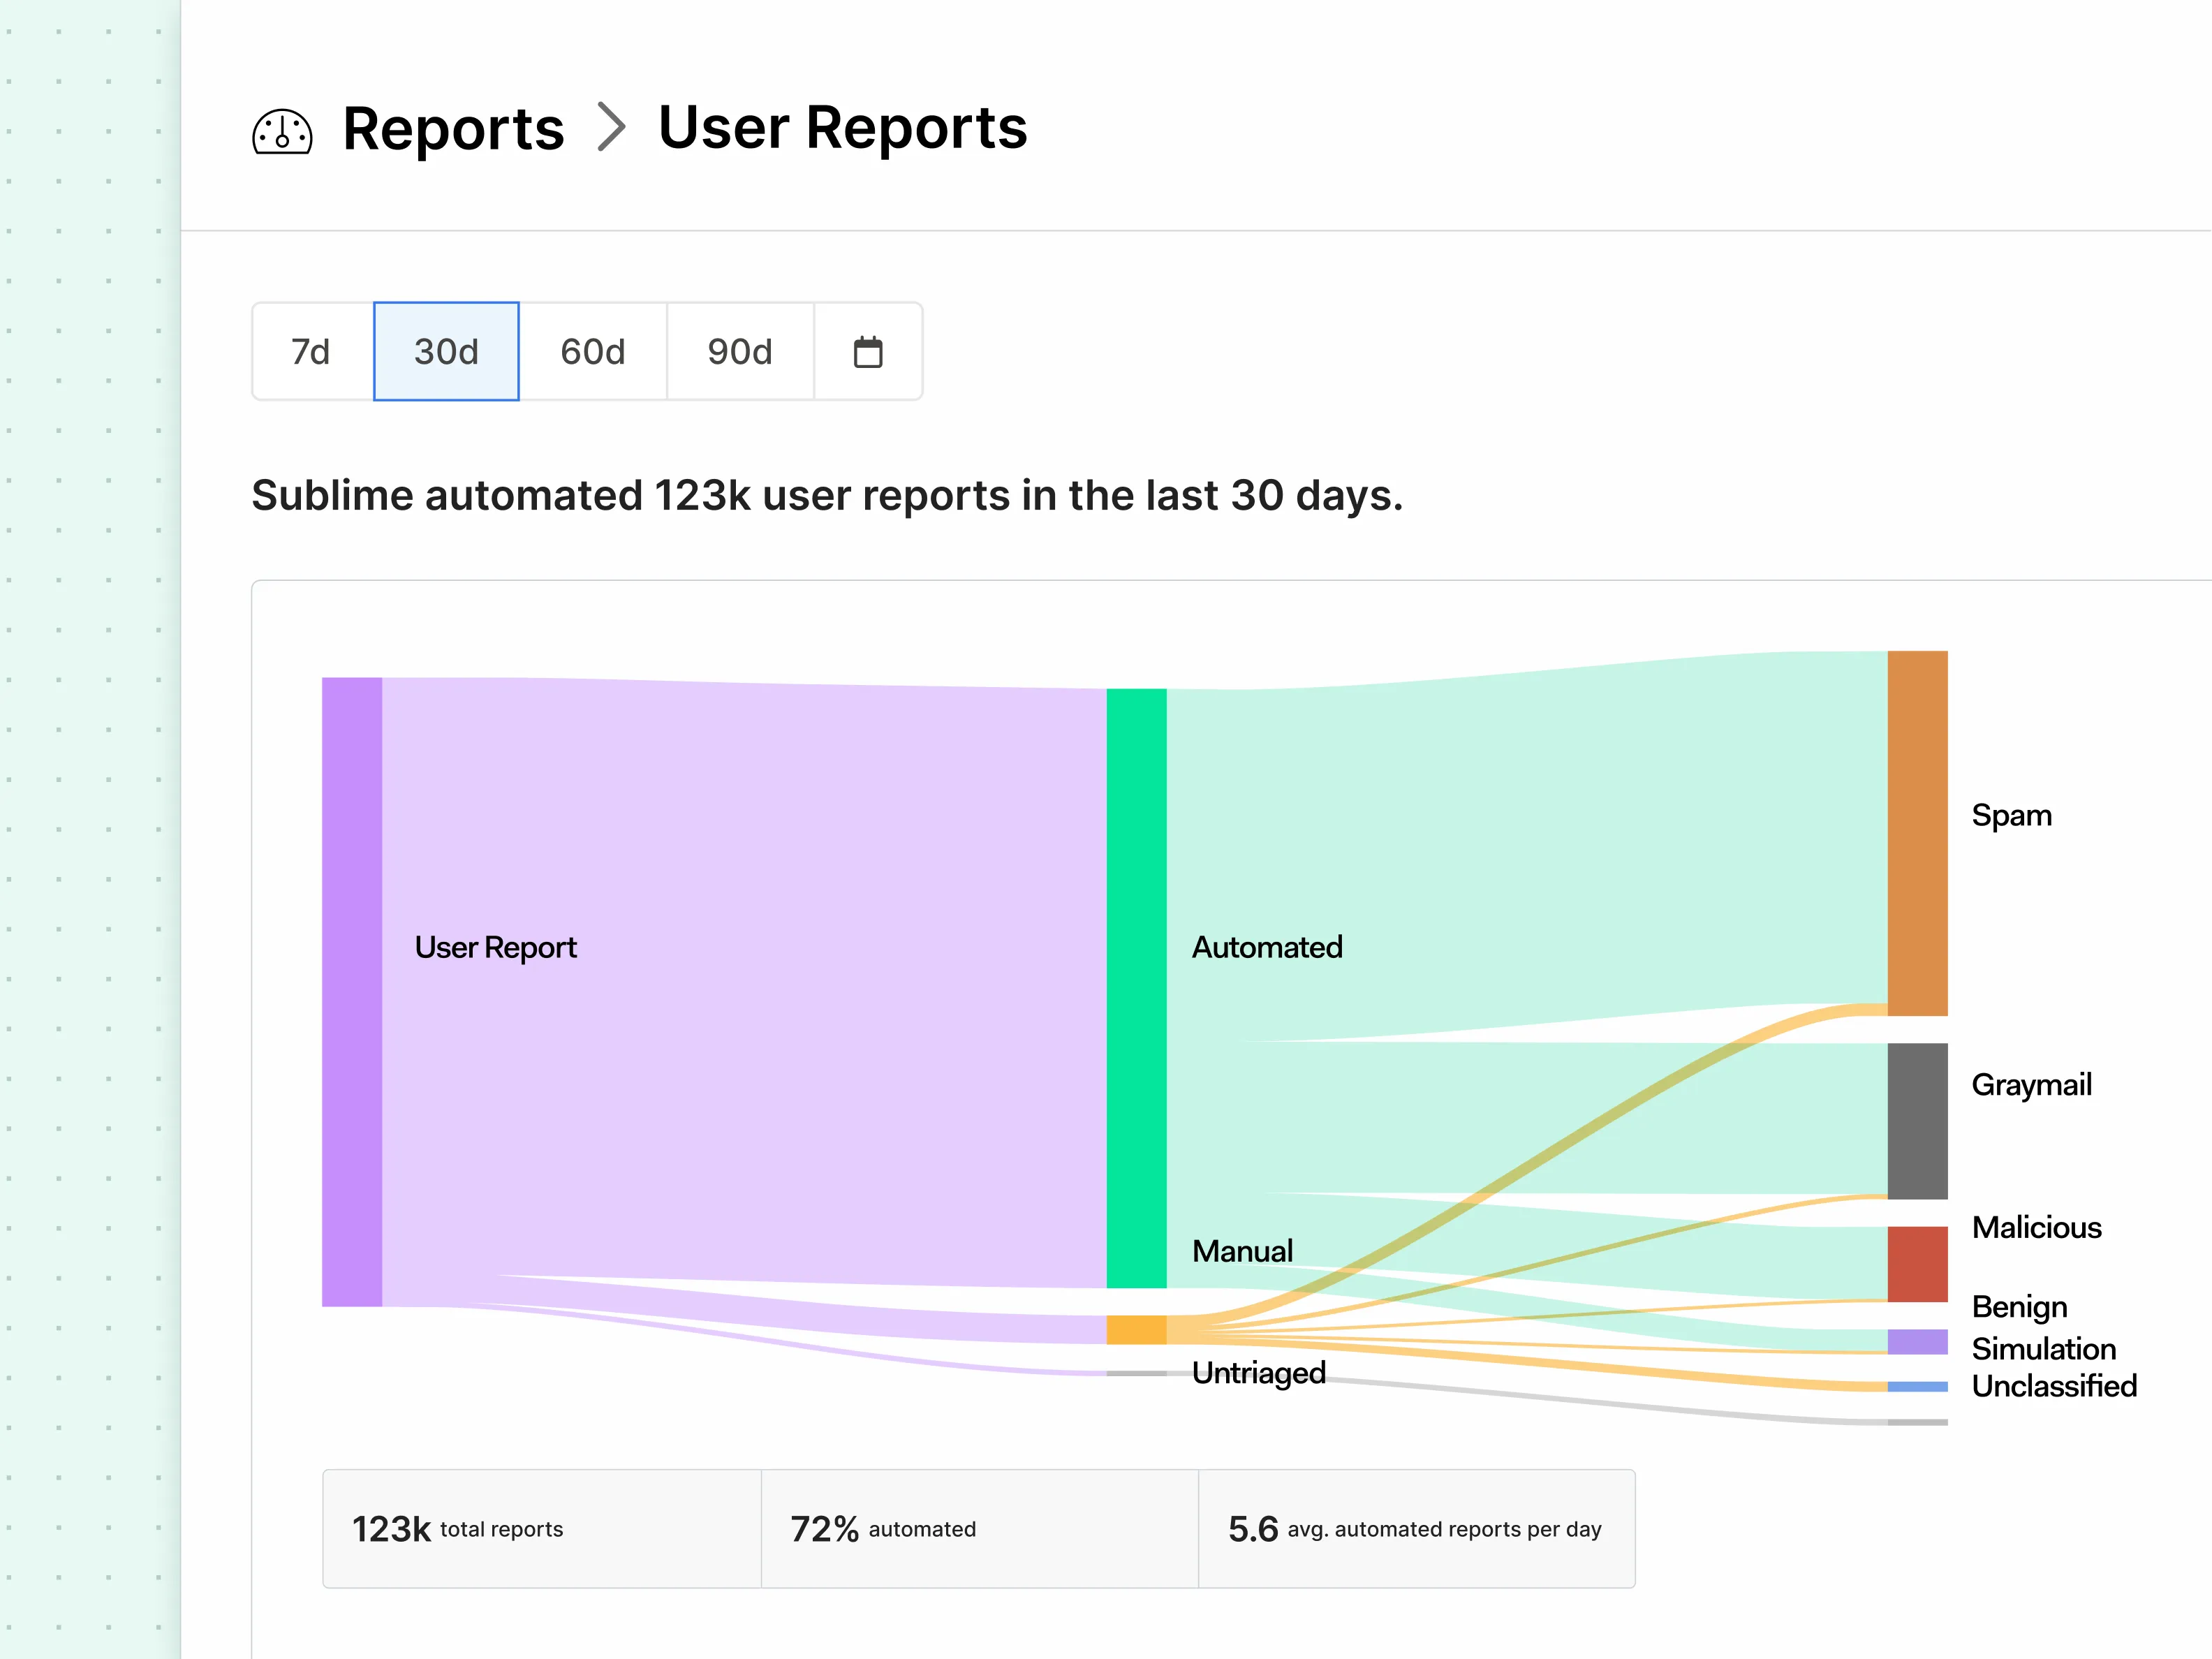
ASA, our AI-powered Autonomous Security Analyst, fully automates triage and remediation of user-reported emails.
Self-healing coverage
ADÉ, our Autonomous Detection Engineer, takes ASAs results and creates new detections to close coverage gaps for novel attacks.
Sublime is one of those tools that just works. Everyone's a winner. Employees are happy their emails work, InfoSec has less operational burden, it requires little management, and the tool is nice to use.
Streamline responses to user reports with autonomous, AI-powered analysis, triage, and coverage.
ASA uses the same threat indicators, primitives, and TTPs that a human analyst would to make decisions – only faster.
ADÉ takes results from ASA and creates new coverage, so you don’t have to. After a detection has been autonomously written, backtested, iterated upon, and finalized, a human analyst is notified for final review before it’s added to your instance of Sublime.
Sublime’s abuse mailbox automation lets analysts spend less time in triage.
With Sublime's AI agents and automatic responses for user reports, teams can automatically interact with and give feedback to end-users.

Executives and other high-value targets get extra protection, including custom alerts via API and webhooks.
Sublime automatically quarantines new messages that match previous user reports by grouping similar content.

Abuse mailbox dashboards help security teams identify gaps that need to be filled with updated detections, handling, or user training.

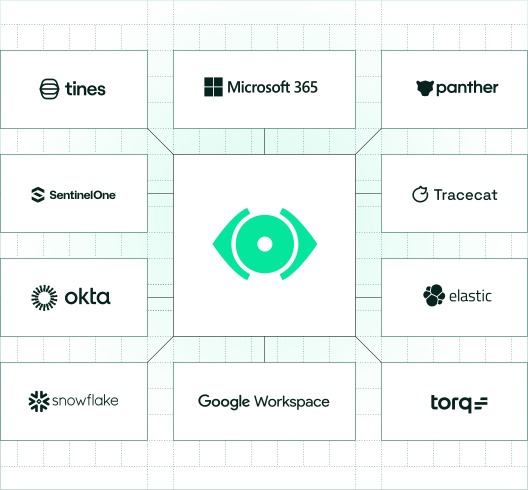
Integrate seamlessly with existing SOC workflows and SIEM platforms.
Sublime offers a wide range of features to detect and prevent email attacks.
Build custom workflows and integrations with comprehensive API access.
Automatically cluster related attacks to understand threat patterns and accelerate response.
Process multiple flagged messages simultaneously based on Rule matches.
Build tailored detection logic for your organization's specific risk profile.
Monitor security posture with customizable reporting and threat visibility.
Analyze sending patterns, authentication failures, and hosting providers.
Safely isolate suspicious messages with one-click remediation and release capabilities.
Integrate seamlessly with existing security orchestration and response tools.
See how Sublime's intelligent email security platform can reduce MTTR and automate your abuse mailbox workflows.
Yes, Sublime's intelligent email security platform offers robust APIs and webhooks for seamless integration with SIEMs, SOAR platforms, and other security tools in your existing stack.
Automated email security reduces manual triage time by up to 90%, allowing SOC teams to focus on strategic initiatives while the AI handles routine abuse mailbox tasks with consistent accuracy.
Most organizations can deploy Sublime within days. Cloud-based deployment enables rapid implementation with minimal infrastructure changes required for immediate threat protection.
Sublime’s agentic email security deploys a team of specialized AI agents – like an analyst and a detection engineer – that work together to protect, triage, and adapt your defenses in real time.
Machine learning email security adapts to new threats in real-time, learns from analyst decisions, and processes vast amounts of data to identify subtle attack patterns that rule-based systems might miss.
See how Sublime delivers autonomous protection by default, with control on demand.