

Inside the surge in ICS phishing: Real attacks and how Sublime caught them

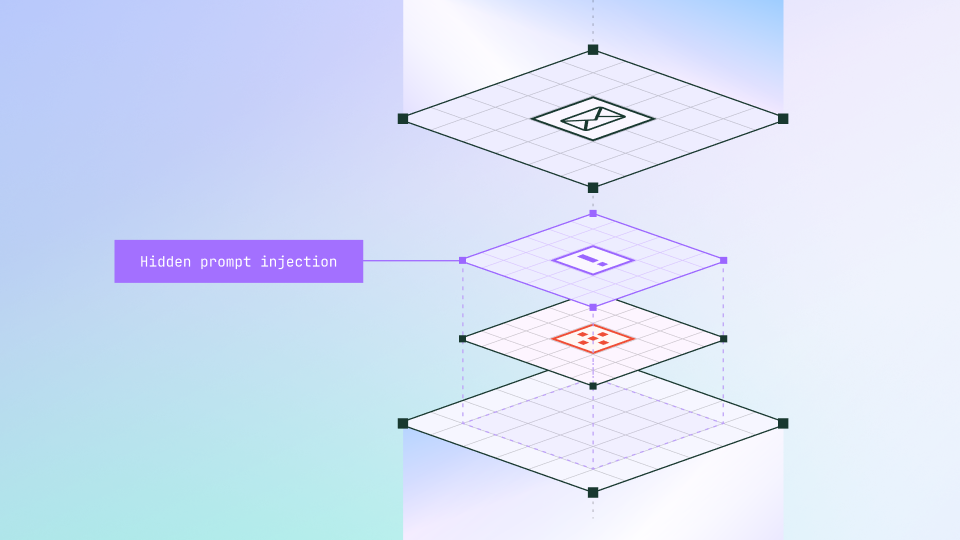
Since August, Sublime’s Detection Engineers have tracked calendar-based attacks growing by more than 1,000% month over month. The reason is simple: a meeting invite reaches targets twice, in the inbox and on the calendar, and most email security products only watch the inbox. Even when the email is caught, the invite can sit in the calendar. The invites arrive from trusted Gmail and Google Calendar infrastructure, link to free services, and cost the attacker nothing to send.
Join Luke Wescott, Threat Detection at Sublime, and Randy Pargman, Head of Detection at Sublime, as they break down what is driving the surge, then walk through real attacks Sublime has caught. For each one, you’ll see the red flags that gave it away and how Sublime followed the trail from the malicious email to the malicious calendar entry.
What you’ll learn
- Why calendar-based attacks are accelerating and why tools built for the inbox miss them
- What real ICS phishing attacks look like, from the lure to the payload, and the red flags to train your team to spot
- How Sublime’s detections catch these attacks and remediate the malicious email and the calendar event together
- Practical steps to close the calendar gap in your own environment
Save your spot to see the attacks and the detections that stop them.
Register for Event
Speakers


Now is the time
See how Sublime delivers autonomous protection by default, with control on demand.