

Microsoft gets the first shot at the email, and Sublime acts as the next layer. That combination gives us much better visibility and much more precise detection.
Overview
Centrica is a global energy and services company whose portfolio includes British Gas and Bord Gáis Energy, supporting millions of residential and business customers through a large, distributed workforce where email is critical to day-to-day operations. As phishing campaigns and socially engineered attacks became more sophisticated, the security team needed to improve both the speed and adaptability of its email defense strategy while continuing to support the business efficiently.
Like many enterprise organizations, Centrica already had foundational protections in place through Microsoft. But as threats became more targeted and dynamic, the team recognized the need for more transparent, organization-specific detection coverage and faster response capabilities.
With Sublime running alongside Microsoft, Centrica investigates threats faster and closes coverage gaps in hours.
When visibility and adaptability became critical
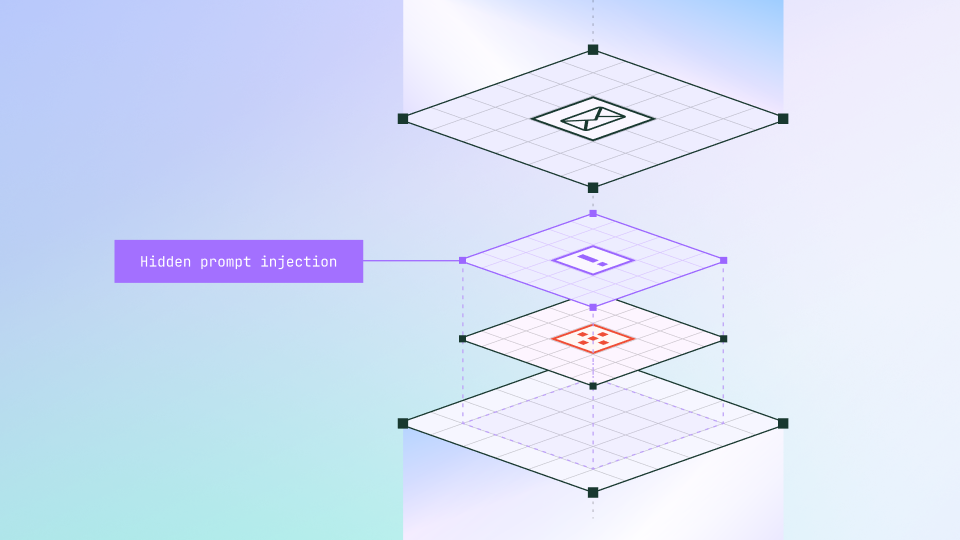
Centrica’s security team began seeing phishing emails that hid QR codes inside PDF and DOCX attachments, sending recipients to credential-harvesting pages. The technique moves the malicious link out of the message text and into an image, where conventional filtering was never built to look. Microsoft’s native filtering was not catching these attempts consistently, and the variants changed faster than the team could update its policies.
That gap sat on top of an email security estate that was already substantial: Exchange Online Protection, Microsoft Defender for Office, and an earlier specialist control, all feeding the team’s Sentinel and ServiceNow workflows. The problem wasn’t a lack of tooling. No single layer was catching everything, and the team couldn’t see why a QR-code lure had gotten through or adapt quickly enough to stop the next variant.
“We were identifying more sophisticated phishing attempts coming through, especially things leveraging trusted infrastructure or targeting specific users,” explained Jonathan Canlas, Senior Threat Detection Engineer at Centrica. “We needed a way to respond to those threats much faster.”
A major challenge was the lack of transparency into how detections worked and how protections could be improved over time. Analysts often had limited insight into why messages were or were not flagged, slowing investigations and making it difficult to adapt protection quickly.
The operational burden quickly grew. Investigations required additional effort, and escalations increased.
At the same time, Centrica’s security organization was focused on broader automation and efficiency initiatives, making scalability and operational efficiency critical evaluation criteria for any new solution.
Adding adaptive protection alongside Microsoft
When Centrica set out to respond faster to new attack techniques, the team looked for greater transparency into how detections work, adaptive coverage, and no added operational complexity. Sublime met that bar when the team first engaged in February 2024. Its API-native integration model required no MX record or mail-routing change and deployed in hours. The deciding factor was the control Sublime offered. Analysts could inspect and tune detection logic directly instead of waiting on vendor support tickets.
As Greg Coutouvidis, Director of Global Infrastructure Engineering at Centrica, put it, “What’s refreshing about how Sublime does detection is that there’s no black box. You read the detection logic and see exactly why it fired, so you’re never taking a vendor’s word for it.”
Sublime also fit into Centrica’s layered strategy, adding detection and response on top of its Microsoft investment instead of replacing it.
A broader evaluation the following year benchmarked Sublime against other options on the market, and Sublime came out on top. Centrica has revisited the market since, and the original choice has held up.
Faster response and stronger operational efficiency
Centrica’s own reporting shows the impact of adding Sublime. In a recent 30-day period, Sublime flagged 783 emails as malicious or suspicious, independent of Microsoft’s verdict. Of those, 99.3% were remediated automatically, and no user clicked through on mail flagged as malicious. Centrica keeps that count separate from its noise reduction so the threat picture isn’t inflated.
The far larger number is the noise. Over the same period, Sublime triaged 642,761 graymail and bulk-outreach messages, plus a further 243,379 likely-benign messages, without analyst involvement. That work used to land in the same queues as genuine threats.
The team also reduced investigation overhead by giving analysts richer context and transparent detection logic, allowing them to make decisions more efficiently and spend less time pivoting between tools. As Canlas explained, ASA (Autonomous Security Analyst) summaries of user-reported emails help analysts quickly understand what action to take and close out incidents faster. Joshua Bignall, GSOC Manager, Cyber Security at Centrica, noted that the richer data available within Sublime has improved investigations into user-reported email and helped reduce downstream escalations.
A recent example shows how quickly the team can respond. A phishing email bypassed existing protections due to a DMARC-related issue. After the message was reported by a user, the team investigated similar emails, identified shared tradecraft, and deployed a new detection combining failed authentication signals with additional message attributes.
Centrica uses ADÉ (Autonomous Detection Engineer) to build detections in response to new threats, which cuts manual testing time and lets analysts concentrate on unique threats.
These improvements have allowed analysts to spend more time on proactive security work and higher-risk investigations instead of repetitive triage and escalation workflows.
Built for evolving threats
Centrica expects attacker techniques to keep changing, and the team is expanding its use of Sublime to match.
One sustained email-bombing campaign, built to bury a genuine malicious message under a flood of mail, became a standing protection. Centrica flagged the pattern to Sublime, and email-bomb protection, which detects sustained spikes to a mailbox and remediates the flood automatically, is now active in its environment. The next campaign is remediated automatically.