

Sensitive data travels over email every day. Most of these messages are important for the proper flow of day-to-day business, but sometimes an employee sends sensitive information to someone who shouldn’t have it. Other times, an insider or attacker sends it out deliberately.
Traditional DLP is supposed to catch messages that violate policy without blocking the rest, but it rarely does. Rigid rules and AI classifiers miss the context behind a message and flag things that were never a problem. These opaque detections are hard to understand and harder to tune, so teams loosen policies until the program has holes or sit in monitor mode because nobody wants to be the person who blocked the quarterly close.
Inbound threats and outbound data loss also end up in separate tools, with separate detection logic and workflows.
Sublime Email DLP is generally available, making Sublime the first platform to deliver agentic security for both inbound and outbound email. ASA (Autonomous Security Analyst), the same AI analyst that investigates inbound attacks, now reviews every flagged outbound message before delivery, using detection logic you can read.
"Sublime's Email DLP lets us tailor detections to our own risk areas, instead of waiting on a vendor to respond. Knowing exactly why something gets flagged gives us the confidence to keep closing gaps as new risks come up."
– Senthil Kumar Iyyappan (SKI), CISO and Head of IT, Ocrolus
Prevent sensitive data loss, not legitimate email
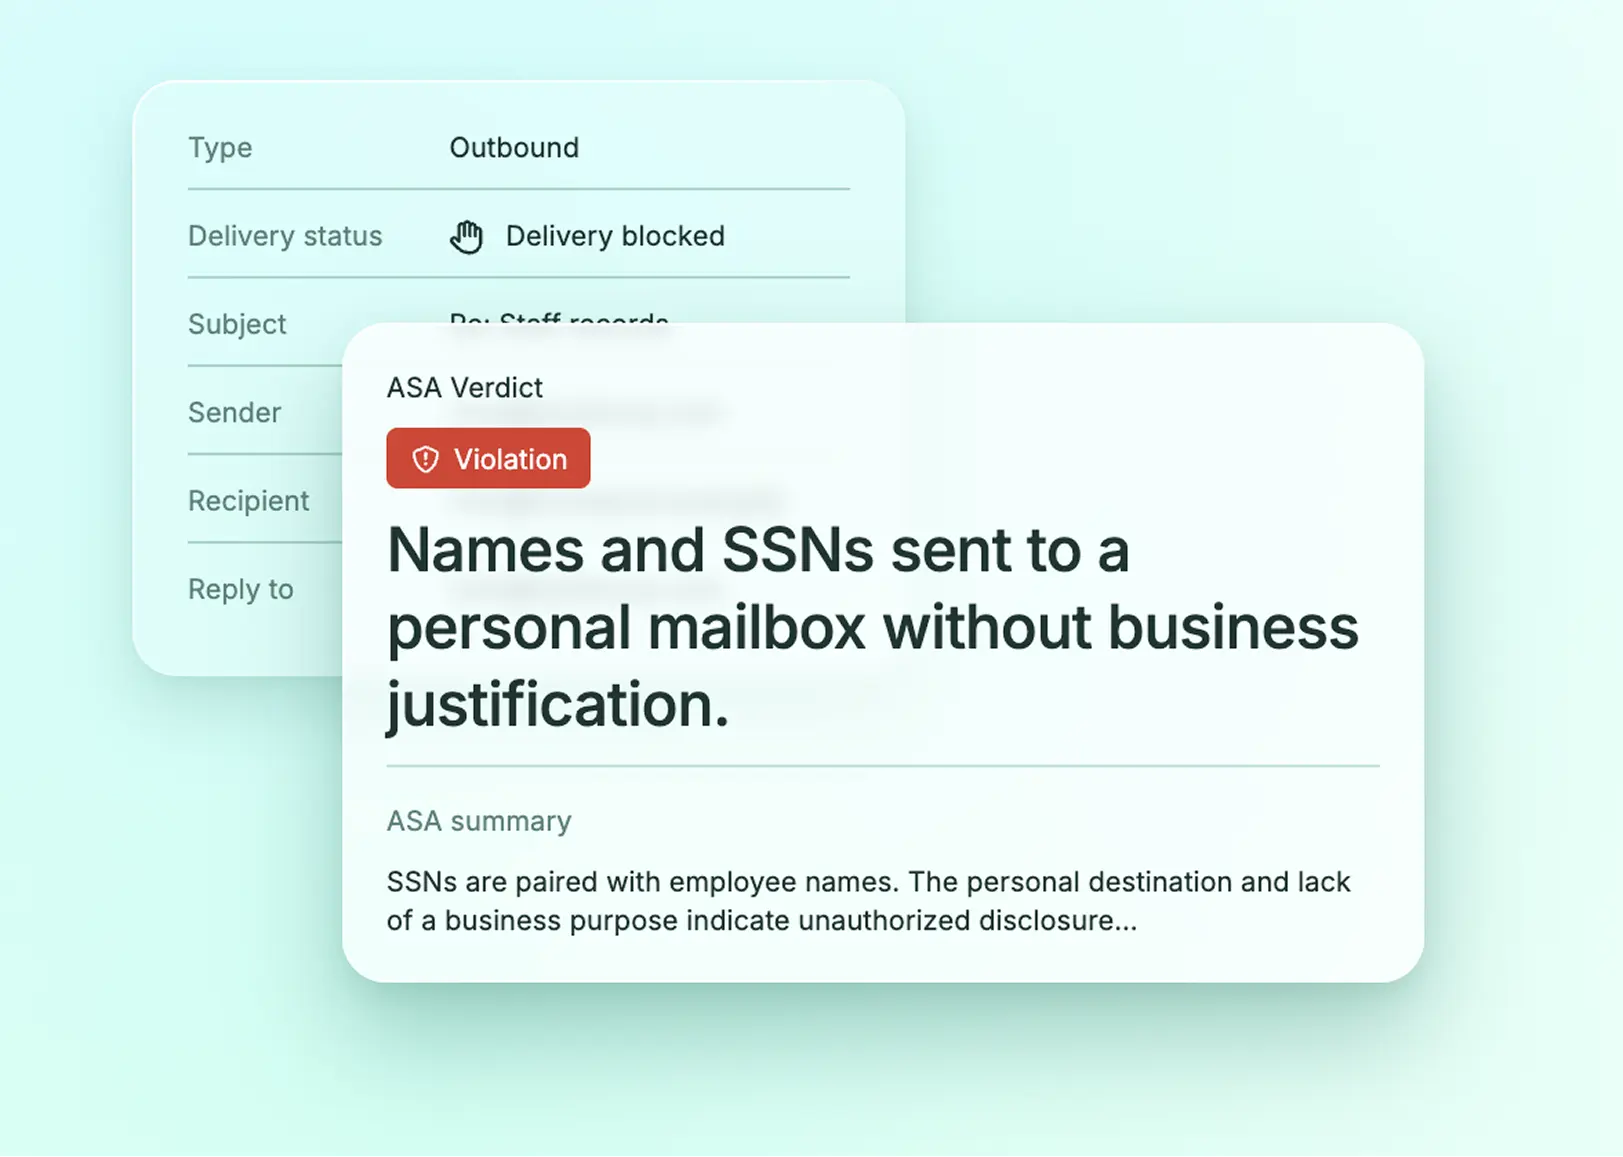
Sublime analyzes every outbound message before it is delivered. When a message matches a policy, ASA (Autonomous Security Analyst) investigates it in full context and reaches a verdict: a violation is blocked, a benign message is released, and a human can decide how to handle anything uncertain. As Sublime adapts, ASA can close more investigations without a person ever touching them.
Before enforcing a policy, ASA can investigate and classify matching messages in monitoring mode without affecting delivery, so you can see exactly what the policy would do.
One platform for every direction email moves
Sublime runs agentic security for inbound and outbound email on one platform. Both directions share the same detection engine, automations, and audit logging in one console, and your team tunes DLP detections the same way it already does for inbound.
Detection logic you can read and change
Every verdict traces back to detection logic you can read and adjust, so when a message is blocked, you can see precisely why. For compliance teams, this creates a fully defensible audit trail. For security engineers, it provides the confidence needed to move from alert-only to blocking.
Most DLP programs stall in monitor mode because teams cannot predict what a policy will catch. Detection logic you can inspect and adjust, paired with context-aware triage, lets you turn blocking on and leave it on.
Coverage from day one
Sublime Email DLP ships with a detection feed covering personal data, payment data, healthcare data, credentials, and country- and regulation-specific data.
For Microsoft 365 environments, Sublime reads Purview sensitivity labels carried on the message and uses them in policies out-of-the-box. Teams can keep using Purview for classification while Sublime handles transparent, pre-delivery email enforcement.
When a legitimate message gets blocked
The sender is notified with a plain language explanation of what triggered the block so they have more information as they decide whether or not to request release. An admin then approves release requests and the original message goes out.
Investigating a suspected insider? Sender notifications can be turned off or scoped with exclusions.
What you can do with it
- Turn on blocking without stalling the business. ASA clears false positives before they stop legitimate email, so policies stay in enforcement.
- Stop accidental data loss. Keep customer, employee, and financial data from reaching unauthorized recipients.
- Block intentional exfiltration. Stop insiders, or attackers on compromised accounts, from mailing sensitive information out.
- Protect intellectual property. Keep source code, designs, and strategy documents off outside addresses.
- Enforce compliance controls. Protect regulated data and keep the audit trail that supports requirements like HIPAA, PCI DSS, GDPR, CCPA, and SOX.
Get started
Email DLP is available now as an add-on to Sublime Enterprise for Microsoft 365 or Google Workspace. It deploys through native mail-flow rules without an MX record change, with Sublime-hosted and self-hosted options.
- Already a Sublime customer? Contact your account team to add Email DLP.
- Want the details? Learn about Sublime Email DLP.
- Not a customer yet? Get a demo to see Email DLP stop a live message before it leaves.
Get the latest
Sublime releases, detections, blogs, events, and more directly to your inbox.