- Impersonation: Brand
Attack Types
BEC/Fraud
Callback Phishing
Credential Phishing
Extortion
Malware/Ransomware
Reconnaissance
Spam
Tactics and Techniques
Encryption
Evasion
Exploit
Free email provider
Free file host
Free subdomain host
HTML smuggling
ICS Phishing
Image as content
Impersonation: Brand
Impersonation: Employee
Impersonation: VIP
IPFS
ISO
LNK
Lookalike domain
Macros
OneNote
Open redirect
Out of band pivot
PDF
Punycode
QR code
Scripting
Social engineering
Spoofing
Detection Methods
Archive analysis
Content analysis
Computer Vision
Exif analysis
File analysis
Header analysis
HTML analysis
Javascript analysis
Macro analysis
Natural Language Understanding
Optical Character Recognition
OLE analysis
PDF analysis
QR code analysis
Sender analysis
Threat intelligence
URL analysis
URL screenshot
Whois
XML analysis
YARA
Tactic or Technique: Impersonation: Brand
Brand impersonation is a phishing technique where attackers copy the look and feel of trusted companies to make their emails seem legitimate. They recreate logos, colors, templates, and writing styles to mimic well-known brands like Microsoft, Amazon, or PayPal and convince you to trust the message.
They often use lookalike domains to make the links seem real. That could be a small typo, a character swap, or a URL like secure-microsoft[.]com that looks legitimate at first glance. These tricks are meant to get past your defenses and make you more likely to click or respond.
The goal is usually to steal your credentials or convince you to take some kind of action. But over time, these attacks also make it harder to trust what you see in your inbox. Spotting them means looking closely—at the sender address, the way the message is written, and where the links actually go. The differences are subtle, but once you know what to look for, they stand out.
Blog Posts
Tax season email attacks: AdWind RATs and Tycoon 2FA phishing kits · Blog · Sublime Security
Credential phishing Charles Schwab account holders with 2FA bypass · Blog · Sublime Security
Callback phishing via invoice abuse and distribution list relays · Blog · Sublime Security
Talking phish over turkey · Blog · Sublime Security
Living Off the Land: Callback Phishing via Docusign comment · Blog · Sublime Security
Abusing Discord to deliver Agent Tesla malware · Blog · Sublime Security
QR Code Phishing: Decoding Hidden Threats · Blog · Sublime Security
Call Me Maybe? The Rise of Callback Phishing Emails · Blog · Sublime Security
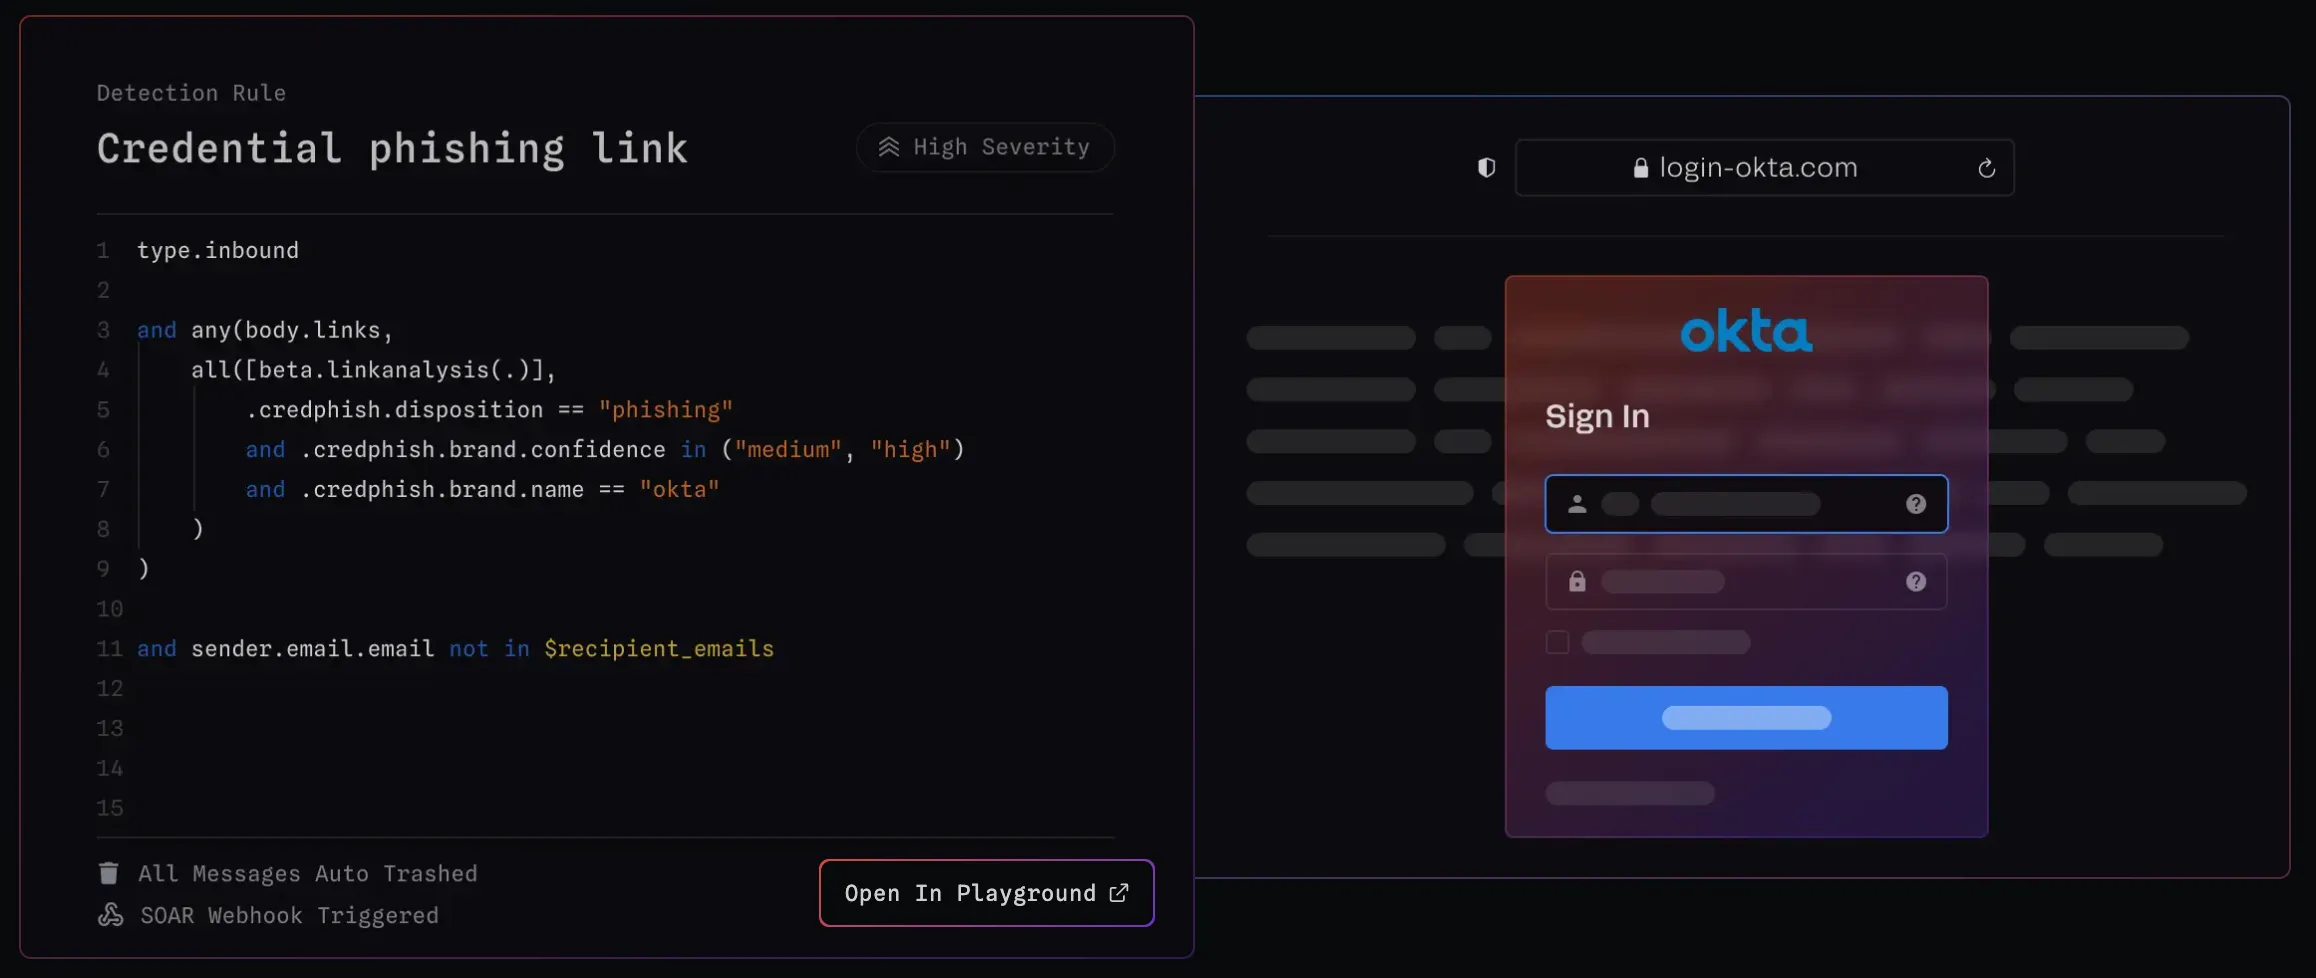
Detecting Credential Phishing using Deep Learning + MQL · Blog · Sublime Security
Detection Methods (19):
Page 1 of 18