- Natural Language Understanding
Attack Types
BEC/Fraud
Callback Phishing
Credential Phishing
Extortion
Malware/Ransomware
Reconnaissance
Spam
Tactics and Techniques
Encryption
Evasion
Exploit
Free email provider
Free file host
Free subdomain host
HTML smuggling
ICS Phishing
Image as content
Impersonation: Brand
Impersonation: Employee
Impersonation: VIP
IPFS
ISO
LNK
Lookalike domain
Macros
OneNote
Open redirect
Out of band pivot
PDF
Punycode
QR code
Scripting
Social engineering
Spoofing
Detection Methods
Archive analysis
Content analysis
Computer Vision
Exif analysis
File analysis
Header analysis
HTML analysis
Javascript analysis
Macro analysis
Natural Language Understanding
Optical Character Recognition
OLE analysis
PDF analysis
QR code analysis
Sender analysis
Threat intelligence
URL analysis
URL screenshot
Whois
XML analysis
YARA
Detection Method: Natural Language Understanding
Natural Language Understanding (NLU) uses machine learning algorithms to analyze and interpret message content, helping systems detect subtle signs of malicious intent. Instead of just matching keywords, NLU looks at the context, tone, urgency, and intent behind the message.
NLU can help you detect:
- Urgent language commonly used in BEC attacks impersonating executives or departments
- Credential theft attempts disguised as legitimate service notifications
- Extortion or blackmail tactics used in intimidation campaigns
- Financial terms typically found in payment fraud or invoice scams
- Deceptive job offers designed to steal sensitive information
For example, NLU can identify when an email uses urgent language ("immediate attention required") combined with financial requests ("wire transfer") and impersonation, which are common tactics in BEC attacks.
Blog Posts
Hiding a $50,000 BEC financial fraud in a fake email thread · Blog · Sublime Security
Callback phishing via invoice abuse and distribution list relays · Blog · Sublime Security
B2B freight-forwarding scams on the rise to evade financial fraud crackdowns · Blog · Sublime Security
Hidden credential phishing within EML attachments · Blog · Sublime Security
Adversarial ML: Extortion via LLM Manipulation Tactics · Blog · Sublime Security
Combating GenAI Email Attacks with BERT LLM · Blog · Sublime Security
Payroll Fraud via LLM-Generated Emails · Blog · Sublime Security
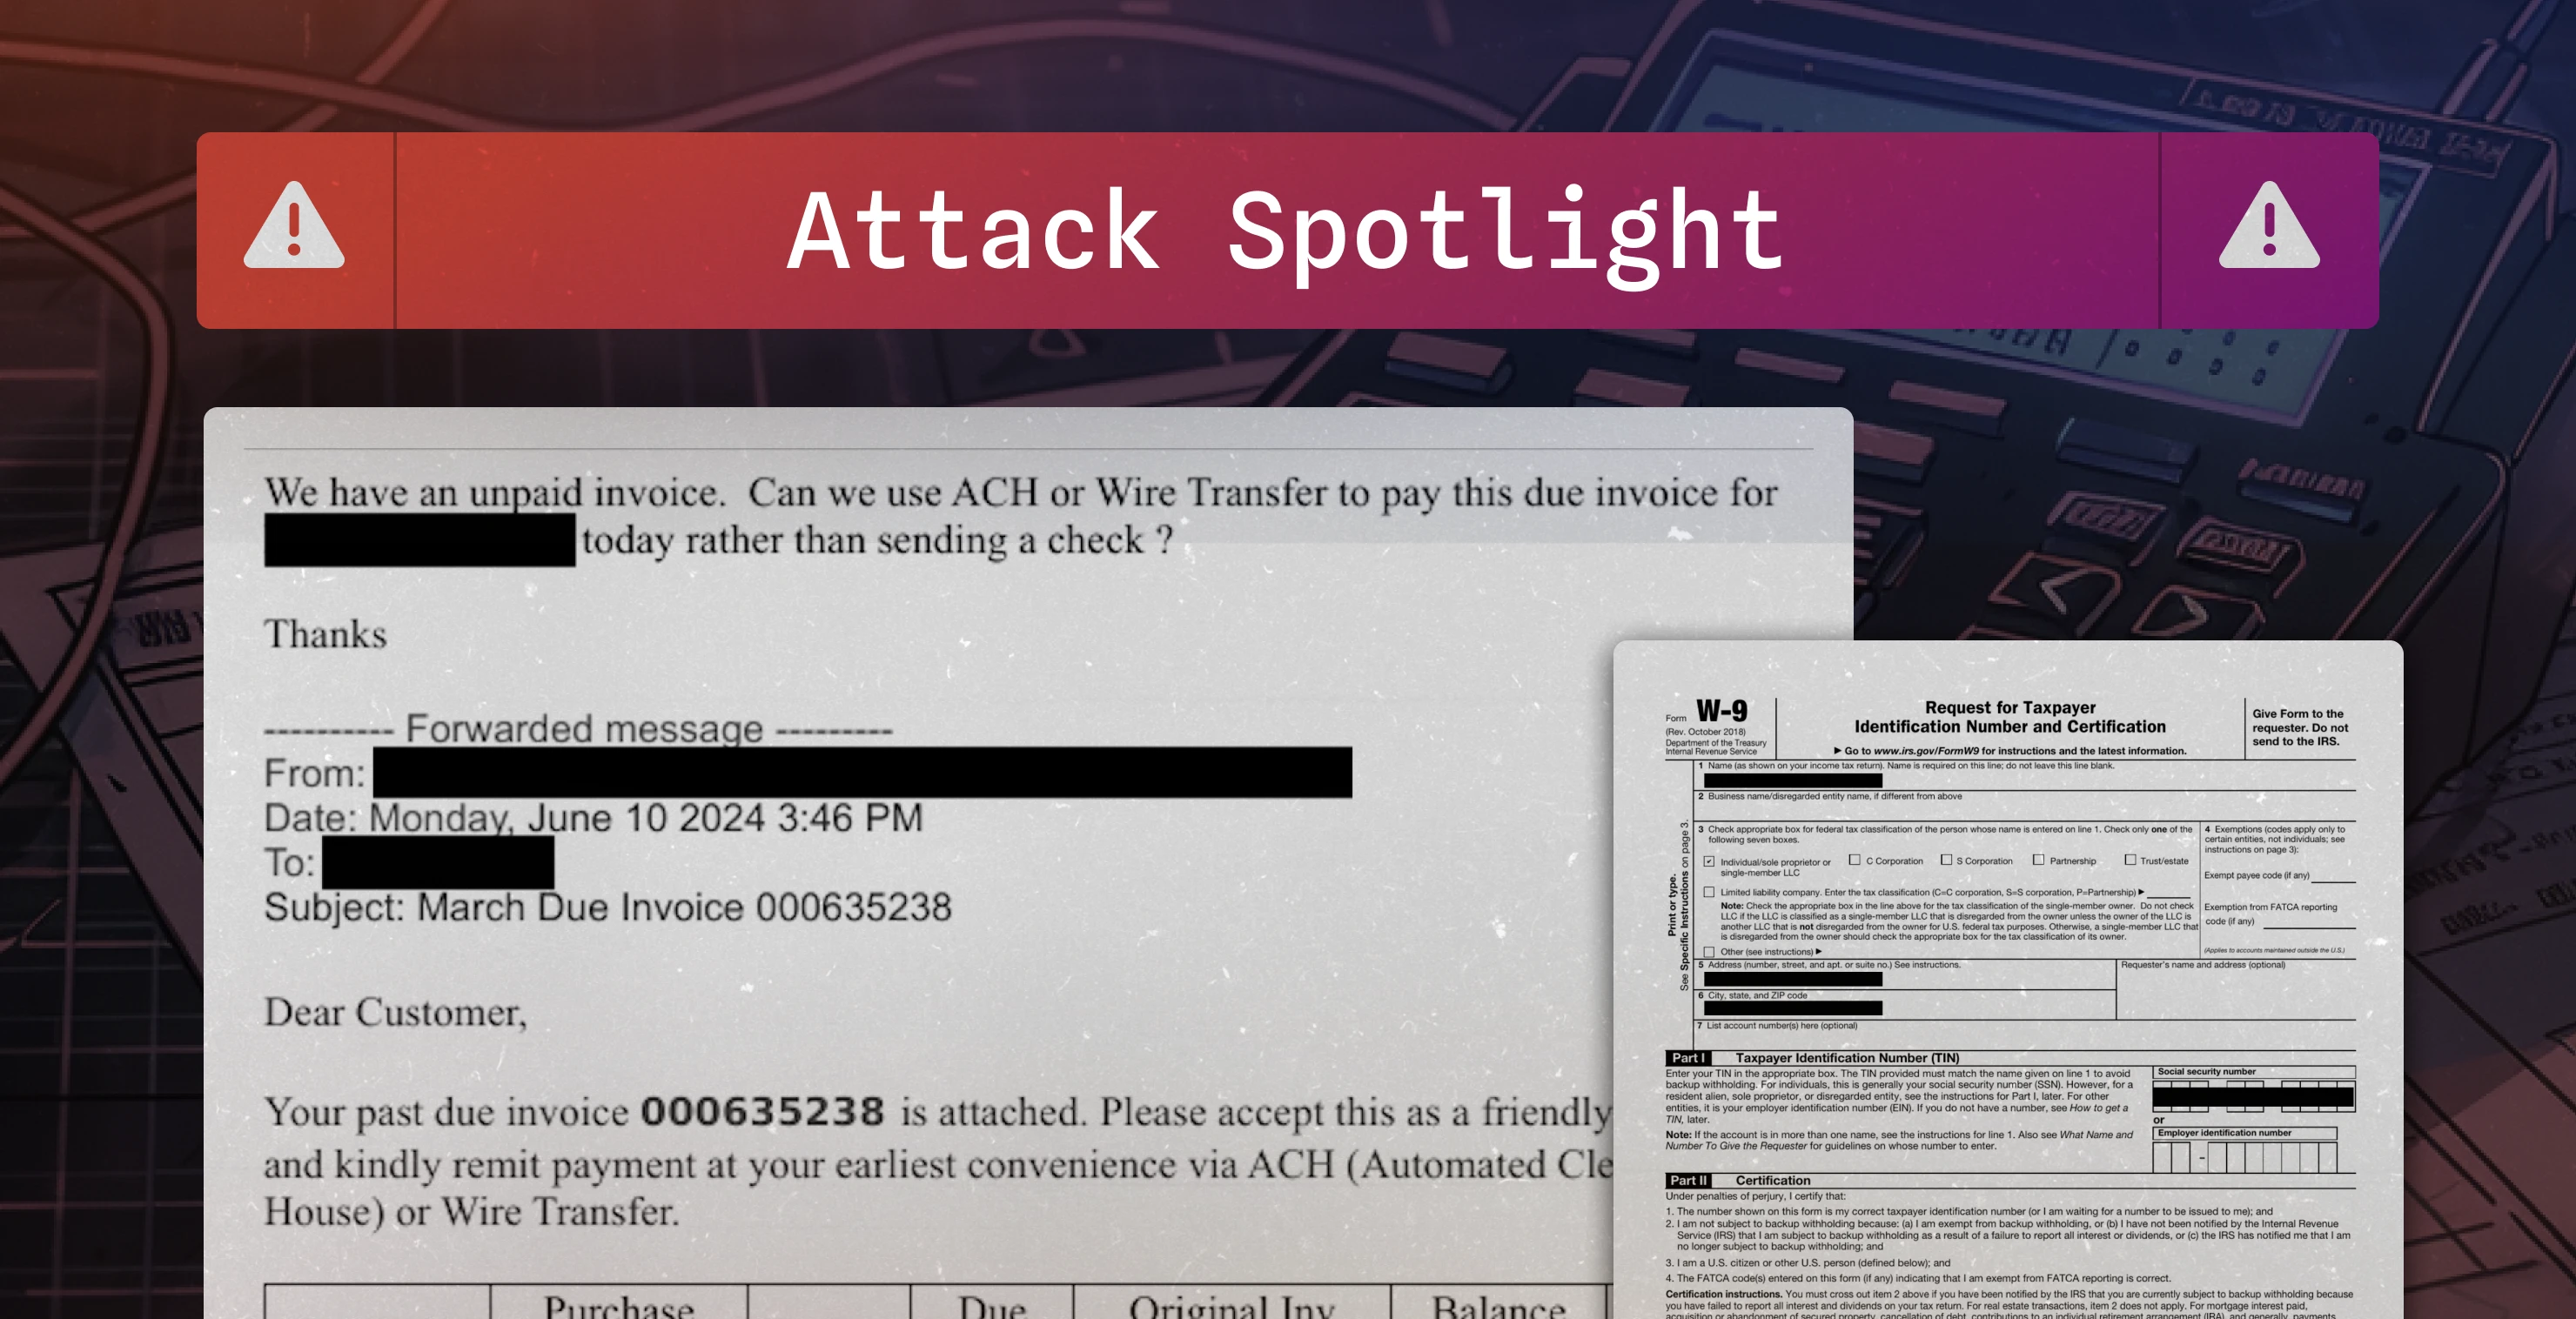
Fake invoice used to conduct $16,800 BEC attempt · Blog · Sublime Security
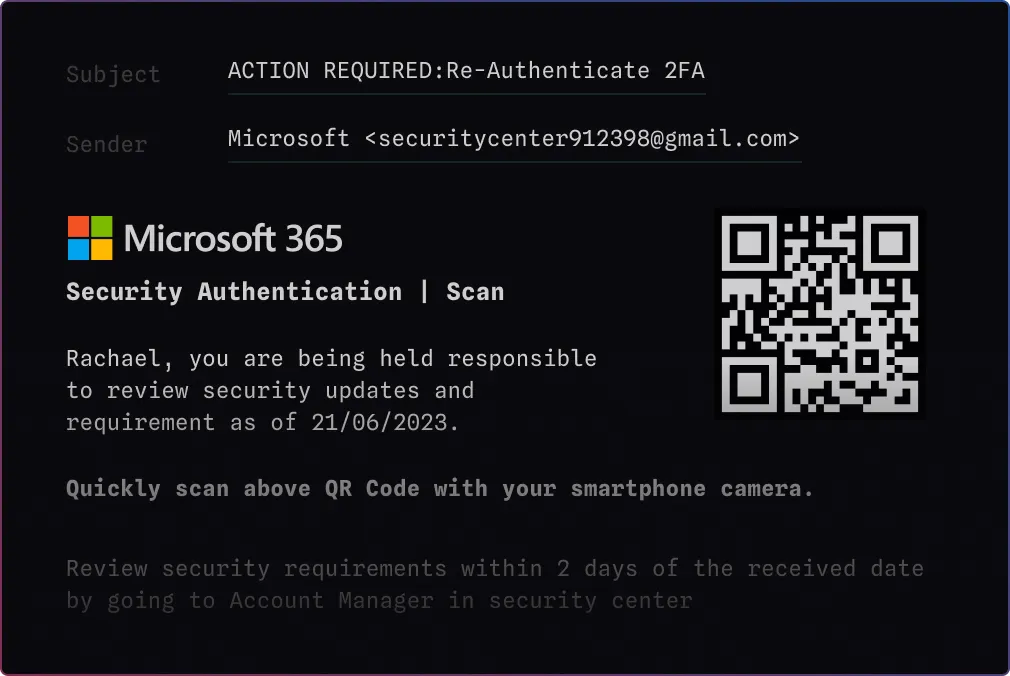
QR Code Phishing: Decoding Hidden Threats · Blog · Sublime Security
Call Me Maybe? The Rise of Callback Phishing Emails · Blog · Sublime Security
Tactics & Techniques (21):
Page 1 of 16