- Image as content
Attack Types
BEC/Fraud
Callback Phishing
Credential Phishing
Extortion
Malware/Ransomware
Reconnaissance
Spam
Tactics and Techniques
Encryption
Evasion
Exploit
Free email provider
Free file host
Free subdomain host
HTML smuggling
ICS Phishing
Image as content
Impersonation: Brand
Impersonation: Employee
Impersonation: VIP
IPFS
ISO
LNK
Lookalike domain
Macros
OneNote
Open redirect
Out of band pivot
PDF
Punycode
QR code
Scripting
Social engineering
Spoofing
Detection Methods
Archive analysis
Content analysis
Computer Vision
Exif analysis
File analysis
Header analysis
HTML analysis
Javascript analysis
Macro analysis
Natural Language Understanding
Optical Character Recognition
OLE analysis
PDF analysis
QR code analysis
Sender analysis
Threat intelligence
URL analysis
URL screenshot
Whois
XML analysis
YARA
Tactic or Technique: Image as content
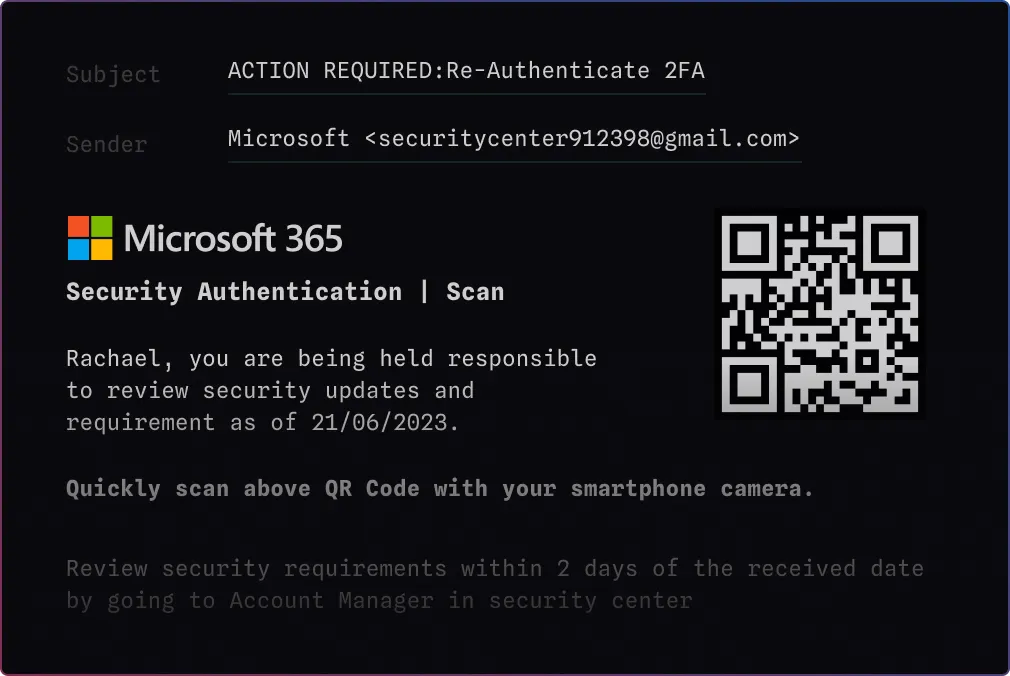
Phishing attacks sometimes use images instead of text to hide their intent and evade detection. This technique, often called “image as content,” involves embedding fake login prompts, alerts, or messages inside graphics that look legitimate but can’t be scanned by traditional text-based filters.
These images often appear polished and professional, using logos and layouts that mimic real companies. In many cases, the image itself is clickable and leads you to a phishing site. With little or no surrounding text, the message is more likely to slip through security scans and still look convincing.
This tactic works because visuals feel trustworthy. A branded banner or alert can seem more legitimate than a plain-text email. That’s why defending against it is harder. Traditional filters struggle to analyze image content, so stopping these attacks often requires a combination of advanced image scanning and the ability to recognize visual red flags—not just suspicious text.
Blog Posts
Attack Types (5):
Detection Methods (16):
Page 1 of 3